Executive Summary:
Default network access is a silent risk multiplier for modern enterprises. When internal users, third-party vendors, or compromised accounts can traverse your network without friction, a single compromised endpoint exposes your core databases. Network segmentation fixes this by creating enforceable digital perimeters around critical data assets.
Key Takeaways for Enterprise Leadership:
- Access Is Not Entitlement: Physical or remote entry into the network should never grant implicit access to mission-critical database clusters.
- Blast Radius Reduction: Micro-segmentation stops lateral movement, ensuring a breach at the edge remains isolated at the edge.
- Policy over Proximity: Restricting user access levels requires intent-based access policies driven by identity, role, and real-time context rather than simple IP addresses.
- Regulatory Compliance Realized: Granular segmentation streamlines audit paths for HIPAA, PCI-DSS, and SOC 2 by narrowing the exact scope of sensitive environments.
The Default-Trust Illusion in Enterprise Networks
For decades, enterprise IT architecture was built like a medieval castle: thick outer walls surrounded by a deep moat. Once a user passed authentication at the perimeter, they were trusted to roam freely across the internal network.
That perimeter-first strategy is fundamentally broken. In today’s hybrid workplace, the network border is fluid, porous, and constantly shifting. Employees access SaaS applications from home, field engineers connect via guest Wi-Fi, and third-party vendor accounts require routine entry into maintenance systems.
The real danger isn’t just the initial entry—it is what happens next.
When a standard workstation succumbs to a phishing attack or malicious link, attackers immediately initiate lateral movement. They scout the internal network, discover flat subnet routing, and quietly pivot toward the ultimate prize: your core databases. Restricting user access levels through network segmentation replaces this misplaced default trust with intentional, verifiable boundaries.
Deconstructing Lateral Movement and the Flat Network Risk
Why do core databases remain so vulnerable despite heavy investments in firewalls and endpoint security? The disconnect lies between perimeter defense and internal traffic control. In a flat or lightly segmented network, every connected device shares a broad routing path to central servers. If a financial analyst’s laptop lives on the same logical network tier as the core Oracle or SQL database housing customer PII, the only thing stopping an intruder is authentication at the database layer itself.

The Mechanics of Internal Pivoting
Once an attacker gains an initial foothold on a standard user endpoint, they execute routine reconnaissance techniques to map out your infrastructure:
- Port Scanning & Service Discovery: Unrestricted internal subnets allow scripts to identify open database ports (such as TCP 1433 for MS SQL or 1521 for Oracle) across the corporate IP space.
- Credential Harvesting: Tools like Mimikatz extract cached domain credentials from the compromised endpoint’s memory to find accounts with elevated privileges.
- Privilege Escalation & Lateral Traversal: Armed with administrative or service account tokens, the attacker hops from device to device across open internal routes, seeking a path directly to core database hosts.
Intentional Isolation: The Role-Based Micro-Segment
Network segmentation disrupts this kill chain by dividing a sprawling network into distinct, isolated zones.
By inserting Next-Generation Firewalls (NGFWs), virtual local area networks (VLANs), and Software-Defined Networking (SDN) policies between subnets, you enforce strict rules on which user groups, devices, and protocols can talk to database subnets.

A user in Marketing or Human Resources has zero business network paths open to transactional database ports. By restricting access at the network layer, you remove the pathways attackers rely on to move horizontally.
Architectural Principles for Database-Centric Segmentation
Protecting core databases requires moving beyond simple VLAN segregation. True network segmentation coordinates identity, device posture, and network routing to enforce least privilege access.
1. Identity-Aware Micro-Segmentation
Traditional firewalls restrict traffic using static IP addresses. Modern enterprise segmentation binds network access to verified user identities and directory roles. Instead of opening IP ranges, policies state: Only authenticated users in the ‘Database Administrator’ security group, connecting from managed devices, may negotiate SSH or database protocol traffic to Tier-1 database subnets.
2. Protocol Isolation and Jump Box Gateways
Core database ports should never be exposed directly to general user subnets—even for legitimate database administrators. High-security architectures require administrative users to route through dedicated Bastion Hosts or Jump Boxes equipped with Multi-Factor Authentication (MFA) and Session Recording. The network segment hosting the database accepts traffic exclusively from the secure gateway, closing off direct access paths for the rest of the enterprise.
3. Continuous Zero-Trust Verification
Authentication at 8:00 AM shouldn’t guarantee implicit trust at 2:00 PM. Segmented networks continuously evaluate contextual indicators—such as device health, anomalous traffic spikes, or unusual login locations—before allowing packets to pass into sensitive database zones. If an endpoint demonstrates suspicious activity, network controllers automatically isolate that device from accessing adjacent segments.
Architectural Matrix: Flat vs. Segmented Network Enclaves
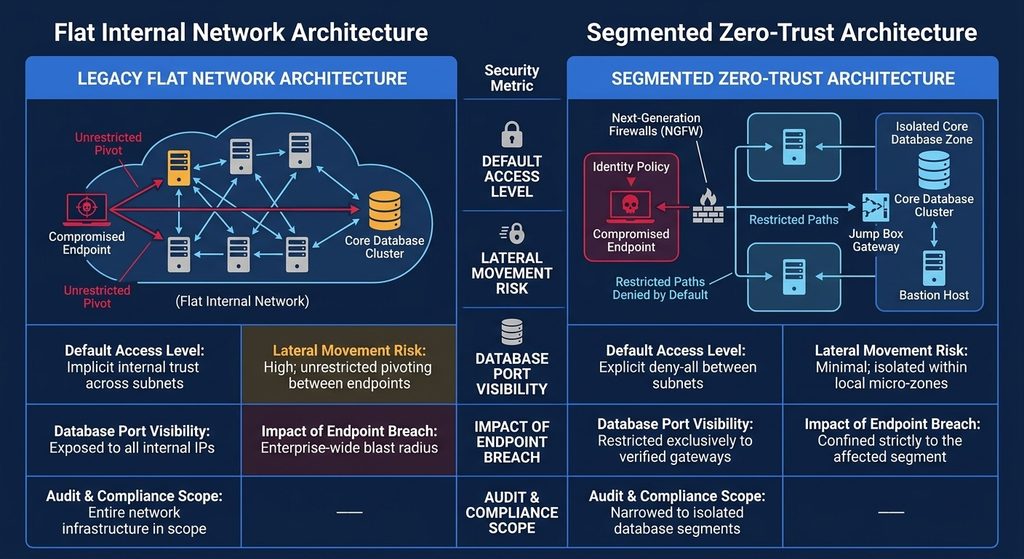
A structured evaluation highlights how transitioning from legacy flat networks to isolated database enclaves fundamentally changes your security posture:
A Strategic Roadmap for Restricting Database Access
Implementing deep network segmentation on a live enterprise network can feel overwhelming. A phased execution plan minimizes operational disruption while methodically hardening your core databases.
Phase 1: Map Traffic and Identify Critical Dependencies
Before blocking a single packet, gain total visibility into existing traffic flows. Deploy passive network monitoring tools to catalog every application, service account, and user role currently querying your core databases.
Phase 2: Establish “Deny by Default” Enclaves
Isolate your critical databases inside dedicated database zones (VLANs or virtual subnets). Implement strict access control lists (ACLs) and firewall rules that block all inbound traffic to these subnets by default, leaving open only verified operational paths.
Phase 3: Enforce Role-Based Access Controls (RBAC)
Integrate your network access controls with your Central Identity Provider (IdP). Define explicit access rules based on job function, least privilege requirements, and device compliance checks.
Phase 4: Monitor, Audit, and Refine
Continuously review denied traffic logs around your database segments. Unexpected connection attempts often point to misconfigured legacy applications, unauthorized shadow IT devices, or early reconnaissance activity.
Protecting critical core databases isn’t achieved by building higher external walls. It comes down to exercising total control over the pathways inside your environment.
When you enforce strict network segmentation and limit user access levels, a compromised laptop remains an isolated incident rather than an enterprise crisis. You protect your organization’s most valuable data assets, simplify regulatory compliance, and build an infrastructure that can safely support modern, flexible work environments.